An attacker has taken around $2 million from the infrastructure connected with Fetch.ai and NuNet.
Both attacks were linked by security firms to the same attacker wallet. Preliminary analysis of Fetch.ai revealed that the attacker used signing credentials that were compromised to gain access to the infrastructure.
While a theft of $2 million may be deemed insignificant in the context of an estimated $2.85 trillion crypto market, what is remarkable about this particular event is that compromised privileged credentials gave the hacker access to critical infrastructure and highlighted how weaknesses in key management can spill across connected systems even if those underlying token contracts are not compromised themselves.
The same wallet drained FET and received the NTX mint
According to PeckShield, the hacker siphoned off a total of 8.7 million FET, valued at an equivalent of $1.53 million, and unauthorizedly minted 408.5 million NTX worth around $462,730.
Blockaid has separately observed about $1.56 million in FET removed from a converter, along with approximately $452,000 in newly minted NTX. This brought the total value of this wallet cluster to about $2.01 million while the attack was ongoing. A follow-up post connected the NTX mint to the same receiving wallet.
🚨Blockaid detected an ongoing exploit on @Fetch_ai on Ethereum.
The same exploiter wallet then received a large NTX mint from the @nunet_global deployer account.~$2.01M so far (~$1.56M FET drained from the converter + ~$452k NTX minted) across the cluster. Attack still…
— Blockaid (@blockaid_) September 19, 2026
NuNet is also part of the same broader AI-crypto ecosystem. CoinMarketCap describes it as the second spin-off from SingularityNET.
The weak point was privileged authorization
According to the presented evidence, it cannot be concluded that a single key was responsible for both projects. Based on Fetch.ai’s preliminary analysis, it is likely that the signing key had been compromised. On the other hand, the analysis thereof that was done on the blockchain implies that the minting key from NuNet may also be compromised.
In its analysis, SlowMist reported that the TokenConversionManagerV3 relied on only the ECDSA signature from a single externally owned account to authorize the conversionIn() function at the draining of the FET.
The said function did not implement a checkLimits(amount) control mechanism against the transaction, and did not check if burn or lock proofs were available on-chain. The drain of the FET happened as soon as the authorizer key was compromised, since a legitimate signature was all that was required for the draining of the converter’s FET balance.
Fetch.ai said it worked with SingularityNET to deactivate affected wallets and contracts. A later update said no Fetch.ai contracts were then at risk and AGIX-to-FET conversions had been paused as a precaution.
An on-chain analysis of the exploit is now available on ASI:One. It traces the attack from the compromised signing key to the attacker’s cash-out wallets. This is not the final analysis.
Read the report: https://t.co/W95r50VMaY
Together with @SingularityNET, we have deactivated…
— Fetch.ai (@Fetch_ai) September 20, 2026
Why NTX cratered while FET did not
These two tokens responded in distinct ways due to the different effects the attacks had on supply. The FET hack removed previously issued tokens, while the NTX hack generated hundreds of millions of unauthorized tokens, compromising supply integrity and adding extra selling pressure.
According to CoinMarketCap, NTX is currently trading around $0.000066, down almost 95% within the last 24 hours after reaching its all-time low of $0.00004075 on September 20. At the same time, FET’s situation was not complicated by such a catastrophe.
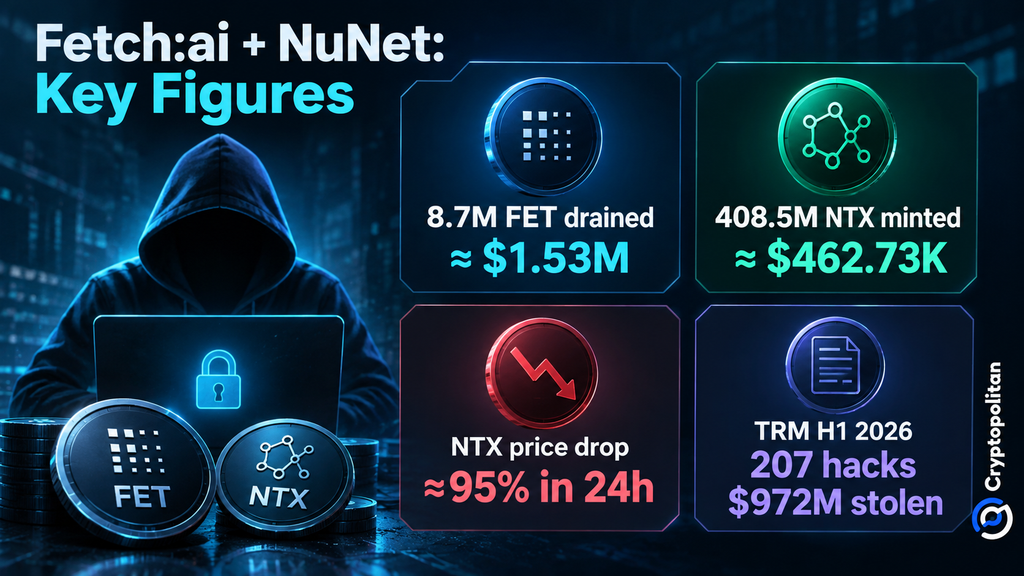
The direct loss is modest, but the attack method fits a much larger industry pattern. TRM Labs recorded 207 hacks and $972 million in losses in the first half of 2026. Infrastructure and operational compromises accounted for only about 15% of incidents but roughly 76% of stolen funds.
CoinGecko’s 2026 security report tells a similar story. Infrastructure and supply-chain breaches caused more than $1.8 billion in losses between January 2025 and July 2026, while private-key compromise remained a major failure point.
Cryptopolitan also reported a similar pattern in June, when Humanity Protocol said exposed private keys contributed to losses of up to $31 million, and its H token fell as much as 90%.
Fetch.ai says the investigation remains open. The next questions are how the credentials were compromised, whether Fetch.ai has rotated or replaced all affected privileges, and how NuNet handles the unauthorized NTX still linked to the attacker.
If you’re reading this, you’re already ahead. Stay there with our newsletter.
This articles is written by : Nermeen Nabil Khear Abdelmalak
All rights reserved to : USAGOLDMIES . www.usagoldmines.com
You can Enjoy surfing our website categories and read more content in many fields you may like .
Why USAGoldMines ?
USAGoldMines is a comprehensive website offering the latest in financial, crypto, and technical news. With specialized sections for each category, it provides readers with up-to-date market insights, investment trends, and technological advancements, making it a valuable resource for investors and enthusiasts in the fast-paced financial world.