
Microsoft says three North Korean hacking groups now use AI in their daily attacks, the highest level on its scale.
Microsoft (NASDAQ: MSFT) rates North Korea’s overall use of AI in hacking as high. The report came out as North Korea is blamed for the biggest crypto theft ever, the $6.36 billion Binance hack.
How are North Korean hackers using AI?
In a report published Thursday, Microsoft Threat Intelligence ranked eight of North Korea’s most active hacking groups on a four-step scale. The steps are emerging, expanding, accelerating and operationalized. “Operationalized” is the top step and means that AI is part of the group’s whole operation.
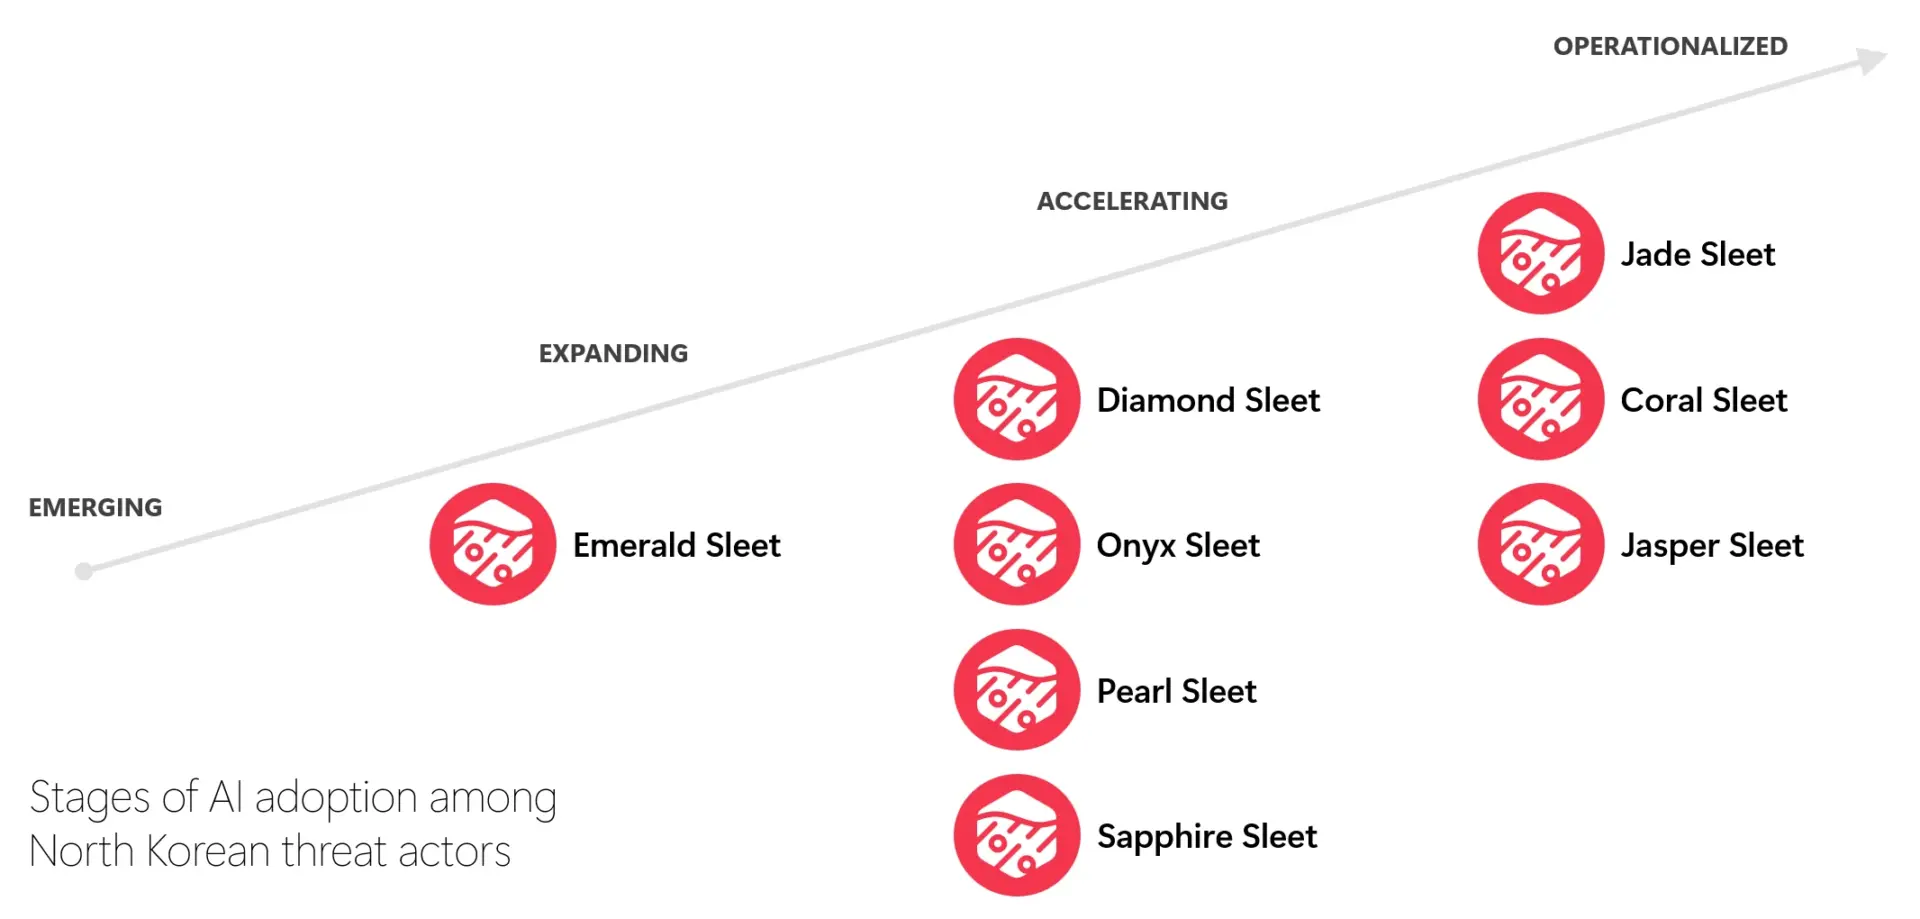
Jade Sleet, Coral Sleet and Jasper Sleet are at the top step while Diamond Sleet, Onyx Sleet, Pearl Sleet and Sapphire Sleet are in the accelerating step. Emerald Sleet is in the expanding step and currently no group is in the emerging step.
Microsoft linked the rankings to specific activity.
- Jade Sleet ran campaigns through three fake companies in a single week.
- Coral Sleet found a way to plant malware in private code storage.
- Onyx Sleet created dozens of custom phishing messages within minutes.
- Diamond Sleet used AI to build fake people and front companies to trick its targets.
One group reportedly made over 100 custom PDF lures aimed at South Korean users in August and September. Work like this once took days for each target.
The groups also used AI coding tools. Microsoft said operators used tools such as Cursor to write code, fix errors and build ways to avoid detection.
Onyx Sleet and Pearl Sleet used ARTEX, an open-source tool that tests systems for weaknesses. It can be linked to an AI model and told to scout targets on its own. A China-linked group, Storm-0940, reportedly used ARTEX against ConnectWise.
Microsoft’s analysts believe humans are still mainly in charge of North Korea’s hacking operations and simply use AI to speed up work the groups already did, such as scouting targets, making phishing content and keeping fake identities going.
Microsoft said crypto exchanges and financial firms are among the most common targets for North Korea’s cyber operations because the aim is mainly to raise money for the regime and gather intelligence.
Did AI play a part in the Binance hack?
So far, there is no evidence yet that the attackers involved in the Binance hack used AI, and Microsoft’s report does not link the Binance theft to any AI technique.
The Binance hack, which has been described as the largest crypto theft on record, happened on October 29. Blockchain research firm TRM Labs said an attacker moved about $6.36 billion out of Binance wallets across ten blockchains, most of it in about 20 minutes.
TRM blamed TraderTraitor, which it calls North Korea’s elite hacking unit, and said it is highly confident in this finding. Jonathan Levin, co-founder of Chainalysis, reached the same conclusion on X.
Cryptopolitan reported that Binance’s own account of the incident outlines how the attackers got in, but not what tools they used. The exchange first said a hacked engineer’s laptop looked like the entry point, but a later probe found more “points of breach.”
Binance has frozen about $3 billion of the stolen funds, paused withdrawals and promised to cover user losses.
The smartest crypto minds already read our newsletter. Want in? Join them.
This articles is written by : Nermeen Nabil Khear Abdelmalak
All rights reserved to : USAGOLDMIES . www.usagoldmines.com
You can Enjoy surfing our website categories and read more content in many fields you may like .
Why USAGoldMines ?
USAGoldMines is a comprehensive website offering the latest in financial, crypto, and technical news. With specialized sections for each category, it provides readers with up-to-date market insights, investment trends, and technological advancements, making it a valuable resource for investors and enthusiasts in the fast-paced financial world.