
I take it back. I was wrong to scoff at the kids.
A few months ago, an article crossed my feeds about wired earbuds. According to my juniors, this retro tech represents elegancy and simplicity—a better time.
I was initially appalled at the characterization. Having lived through tangled wires and multiple snapped cords, I know exactly how Bluetooth headphone dominance came about. But after yet another confirmation of a security vulnerability in a wireless audio device, I’ve been rethinking my position.
Welcome to Safe Mode, your weekly report for pressing security and privacy news—and what steps to take next. Want this newsletter to come directly to your inbox? Sign up on our website!
This particular situation involves Skullcandy’s Dime 3 earbuds. According to Carnegie Mellon University’s cybersecurity response team (CERT), these wireless earbuds will accept pairing requests without user verification. Any nearby, unpaired devices can link with the Dime 3 to record audio input from the microphones, take over audio playback, change the earbuds’ audio profile, or disrupt the user’s connection. If attacked, those who own Skullcandy Dime 3 buds may hear an audio alert of a new device being paired, but may not recognize the significance of the notification.
Skullcandy is not unique in being vulnerable to this kind of flaw—this news follows on the heels of Apple’s Beats Studio Buds and Creative’s Sound Blaster Katana V2X soundbar also falling prey to audio hijacking over Bluetooth. But Skullcandy Dime 3 owners may not have access to a fix. If your pair has older firmware, it remains exploitable. Skullcandy has yet to enable a way to update the buds’ internal software, so that the security patch is applied.
I’m likely not in imminent danger of being hacked through Bluetooth headphones, but I’m mindful of how connected devices can serve as entryways to juicier information. I don’t want someone to listen in my calls, for example.
The easiest solution is to switch to tech that can’t be as easily hacked. Going old-school currently seems the smarter way to go from a cybersecurity standpoint, and in this case, that’s choosing wired devices over wireless. (I’m reminded, as a nerd of a certain vintage, of the phone system in Battlestar Galactica.)
Before, taking this stance would have painted me as an antiquarian (or even a Luddite). But the kids, in their wisdom, have instead made it a smart trend. They really are going to be all right.
In the news
The world is becoming less and less private—and in some ways, less safe by extension. Flock cameras were discovered to take extensive photos of passing cars, OpenAI lets other people see more of your chat prompts than you might think, and Anthropic wants to analyze your financial habits. Each situation sounds innocuous on the surface, but the data shared can reveal much more of your life than you’d want.
Swello / Unsplash
The concerning:
- Ever wonder what lives on a Flock camera? Hackers did and ended up finding roughly 1.6 million images of cars, taken over a three-week period. The cam also had software capable of detecting people, though no facial recognition took place on the camera. (However, this discovery does not prevent such actions happening after photos upload to a central server.)
- Other people may be reading your ChatGPT prompts, according to 404 Media. Called “Project Lily,” the initiative has humans evaluate the chatbot’s responses to prompts. As a result, any sensitive information related to your health, finances, and more could be seen by strangers. Be cautious about what you share.
- Anthropic now supports direct links to bank accounts from within Claude. Called “Claude Money,” it is the latest company to offer financial analysis as an AI chatbot feature. (OpenAI also allows you to link financial accounts to ChatGPT.) Given that chatbot transcripts may not be as private as one would hope (see above), I advise caution in embracing this feature.
The bad:
- Hackers keep putting old attack methods to work. This time, malicious JavaScript is back, installing browser extensions in Chrome and Edge without user approval. If infected, users can leak credentials, fall victim to meddler-in-the-middle attacks, have their activity screenshotted, and more. To protect yourself, don’t manually open JavaScript files.
Tip of the week
Alaina Yee / Foundry
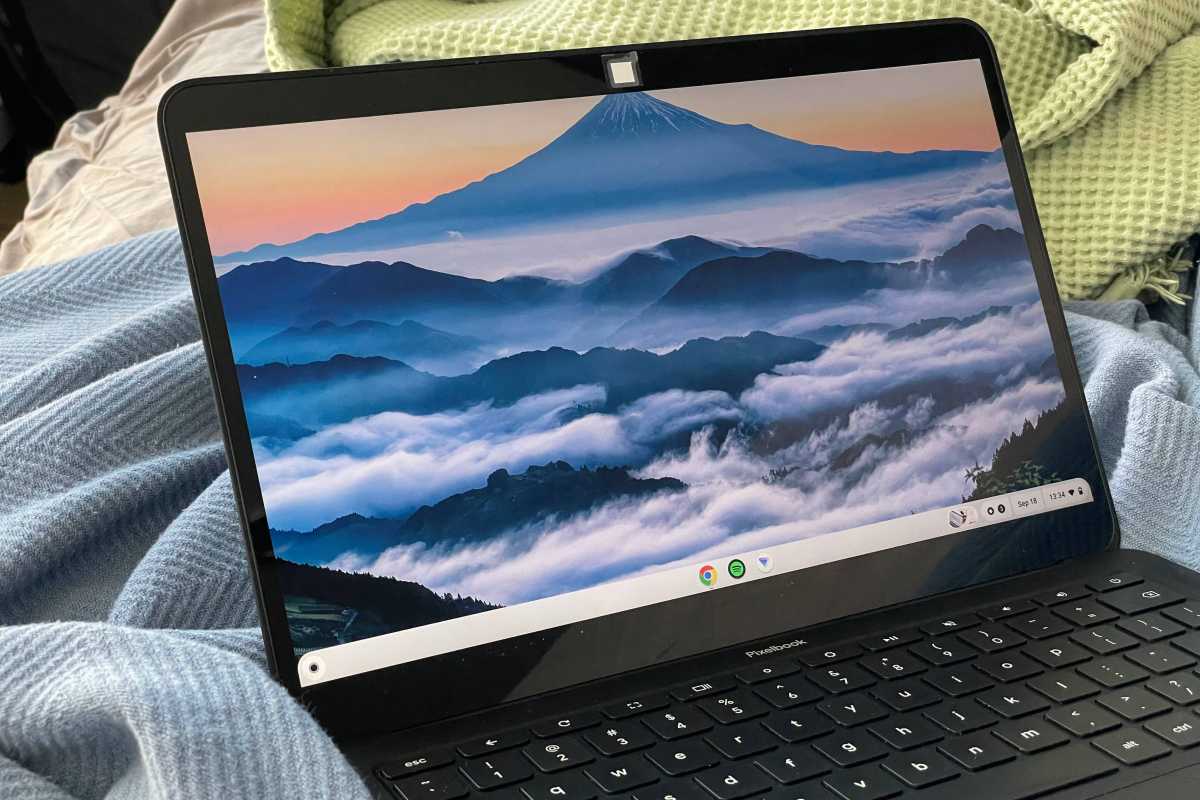
Speaking of low tech solutions to high tech problems—are you worried about someone spying on you through your webcam? You can get back some peace of mind by literally covering the camera on your devices.
You can buy special covers on Amazon and other storefronts for this, but I usually just cut a small square from the sticky part of a Post-It. You can uncover and recover the camera more easily. If I don’t think I’ll ever use an embedded webcam in a laptop, I’ll use a bit of paper and tape.
Note that this won’t solve the underlying cause of being spied on. Run a scan of your system with antivirus software, and also check for any unknown apps or browser extensions.
This articles is written by : Nermeen Nabil Khear Abdelmalak
All rights reserved to : USAGOLDMIES . www.usagoldmines.com
You can Enjoy surfing our website categories and read more content in many fields you may like .
Why USAGoldMines ?
USAGoldMines is a comprehensive website offering the latest in financial, crypto, and technical news. With specialized sections for each category, it provides readers with up-to-date market insights, investment trends, and technological advancements, making it a valuable resource for investors and enthusiasts in the fast-paced financial world.